The case in brief. Court of Appeal of Palermo (Sicily), First Civil Division, judgment no. 1399 filed on 6 October 2025. A municipality had published on its Albo Pretorio (the official notice board every Italian municipality must keep, today online) and on its website documents showing in clear text the name of an employee and information about her health, such as her days of sick leave: among them act no. 4 of 28 April 2009, on display from 23 May to 6 June 2009. Outcome: €7,000 in compensation for non-pecuniary damage, upheld on appeal, plus €2,000 in costs for the appeal, on top of the first-instance costs and the municipality’s own legal fees.
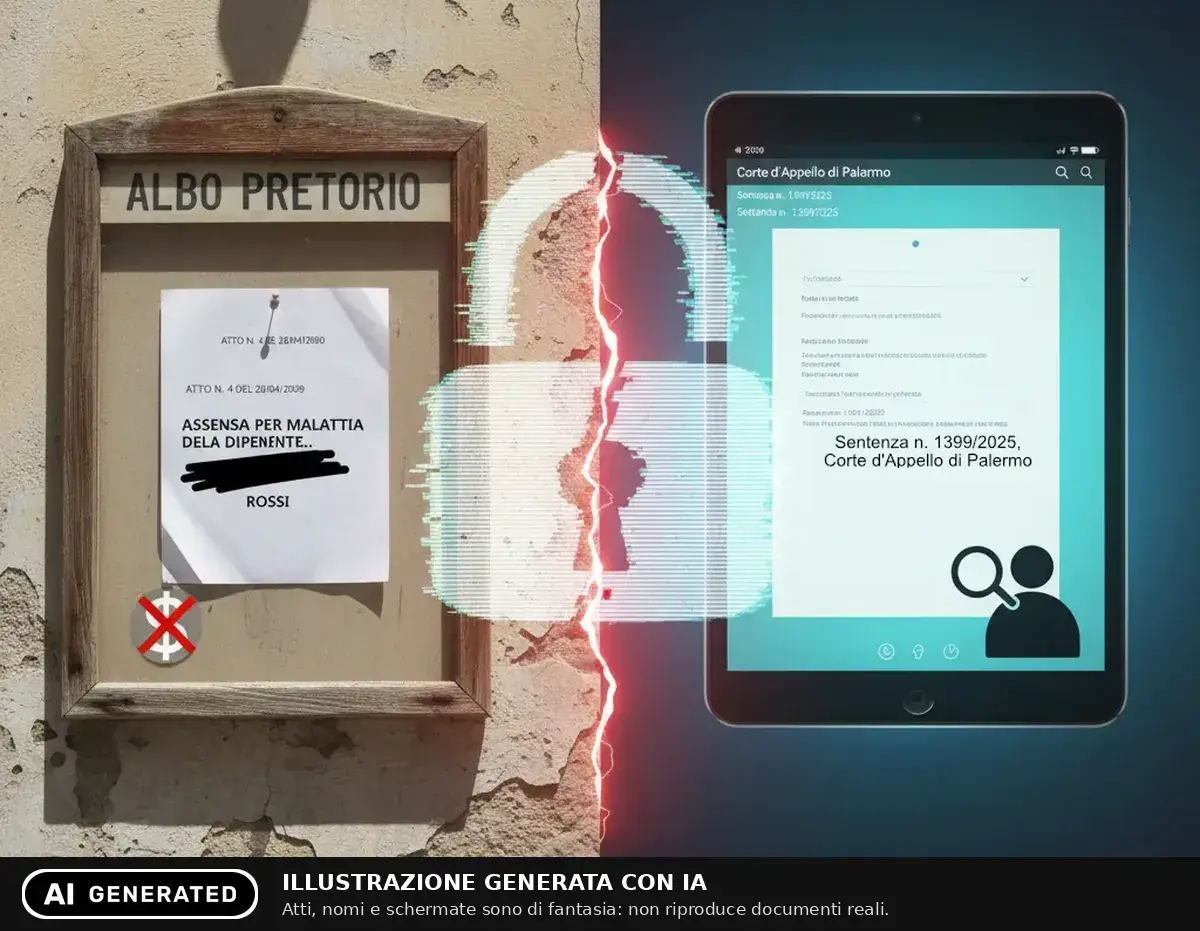
The Court of Appeal of Palermo has upheld a ruling that should make anyone who manages public documents stop and think. An Italian municipality must compensate an employee for publishing administrative acts showing that she had been absent due to illness. No diagnosis, no condition named: her name and the reference to illness were enough. Cost: at least €9,000, not counting the overall legal expenses.
Why this matters outside Italy. The case is Italian, but the mechanism is European. Public bodies across the EU are required to publish many of their decisions, and all of them apply the GDPR, which treats health data as a special category (Article 9) and gives anyone harmed by a breach the right to compensation (Article 82). The names of the laws change; the mistake, and the bill, do not.
The short circuit between transparency and privacy
The paradox is that the municipality thought it was doing its duty: publishing its acts to ensure transparency and make spending traceable. On appeal it defended itself in exactly this way, citing the publication duties in Italy’s consolidated law on local authorities. The problem is that it did it badly.
Transparency duties require certain acts to be made public. But data protection law requires, with equal force, that personal data be protected, health data above all. The facts date back to 2009, so the Court applied Italy’s national data protection code (Legislative Decree 196/2003, known as the Privacy Code) as in force at the time, which already prohibited public bodies from disseminating health data. Today the picture is the same, and even clearer: the GDPR treats health data as a “special category”, and the Italian code, as amended in 2018, repeats that health data may not be disseminated.
The principle is clear, and the Court took it from the Court of Cassation, Italy’s supreme court (judgment no. 18980/2013): publishing an employee’s sick leave on the official notice board or on the institutional website is unlawful dissemination of personal data, even when no specific condition is mentioned. You do not need to go into clinical details to breach someone’s privacy. Revealing that the person was ill is enough.
What it would have taken
The fix was trivial. Instead of writing “absence of employee Rossi due to illness” (the name here is invented), it was enough to write “justified absence” or “absence for personal reasons”. Or to redact the name or the reason and replace it with OMISSIS, the word Italian legal and administrative documents use to mark text that has been left out. The document would have stayed public, the transparency duty would have been met and the employee’s privacy protected. The Italian data protection authority (the Garante) says the same in its 2014 guidelines on the online publication of official documents: data that is not necessary must be redacted or replaced with general wording.
But when you have to handle hundreds of acts a year, human error becomes statistically inevitable. A distracted official, a moment of haste, an outdated document template, and the damage is done: €7,000 in compensation, set by the court on an equitable basis, €2,000 in costs for the appeal alone, plus the first-instance costs and its own lawyers.
The hidden cost of non-compliance
This case dates from 2009, but today the problem is hugely amplified. Official notice boards are online, open to anyone, from anywhere, around the clock. Documents are indexed by search engines. Once a piece of health data is published, even if you remove it after a few days, it may already have been archived, copied and shared.
Italian municipalities publish thousands of acts a year. Companies running public services, publicly owned companies, local health authorities and universities have similar duties. And they all run the same risks: GDPR fines of up to €20 million (how fines apply to public bodies varies from country to country), compensation to the people harmed and, above all, damage to the organisation’s reputation.
The lesson
Data protection compliance is not bureaucracy for its own sake. It is the concrete protection of fundamental rights, but it also protects the organisation.
In this case the Court based the municipality’s liability on Article 15 of the old Privacy Code, which referred to the Italian Civil Code’s rule on dangerous activities (Article 2050). In practice, the employee only had to prove the damage and its link to the publication; it was for the municipality to show that it had taken all suitable technical and organisational measures to prevent it. It is the same logic the GDPR now calls accountability: saying you were careful is not enough, you must be able to demonstrate it.
The municipality could not. And it paid.
Administrative transparency and personal data protection are not in conflict. They must coexist. But that takes structured processes, the right tools and the awareness that, over large volumes of documents, human error is not a remote possibility: it is a statistical certainty.
Do you publish official documents every day? Find the personal data before it goes online.
Request an Omissis demoIt detects personal data in your documents and helps you redact it permanently, leaving the final say to the operator.
For a handful of documents, PDF Editor is enough, free with a free account: redaction happens on your own computer and is irreversible.
Sources and further reading
The sources are in Italian.
- Court of Appeal of Palermo, First Civil Division, judgment no. 1399 of 6 October 2025.
- Eleonora Pergolari, Divulgare lo stato di malattia lede la privacy del dipendente (“Disclosing sick leave breaches the employee’s privacy”), Edotto, 22 October 2025 (with the text of the judgment attached).
- Court of Cassation, First Civil Division, judgment no. 18980/2013, on the publication of sick leave: commentary by Filodiritto.
- Legislative Decree 196/2003 (Italian data protection code), Articles 11, 15 and 22 as applicable to the facts; Article 2-septies in the current version.
- Regulation (EU) 2016/679 (GDPR), Articles 9 and 82.
- Garante per la protezione dei dati personali (Italian data protection authority), guidelines on the processing of personal data in administrative acts and documents published online by public bodies, 15 May 2014.